AIINEWS

AIINEWS

Global intelligence on artificial intelligence and computing

Search Intelligence

Query across our knowledge base of synthesized technology dispatches

Results for “ransomware”4 stories
Update on Synology NAS Ransomware case in Korea: many reports sent to KISA, demanding ransom in bitcoin

Update on Synology NAS Ransomware case in Korea: many reports sent to KISA, demanding ransom in bitcoin

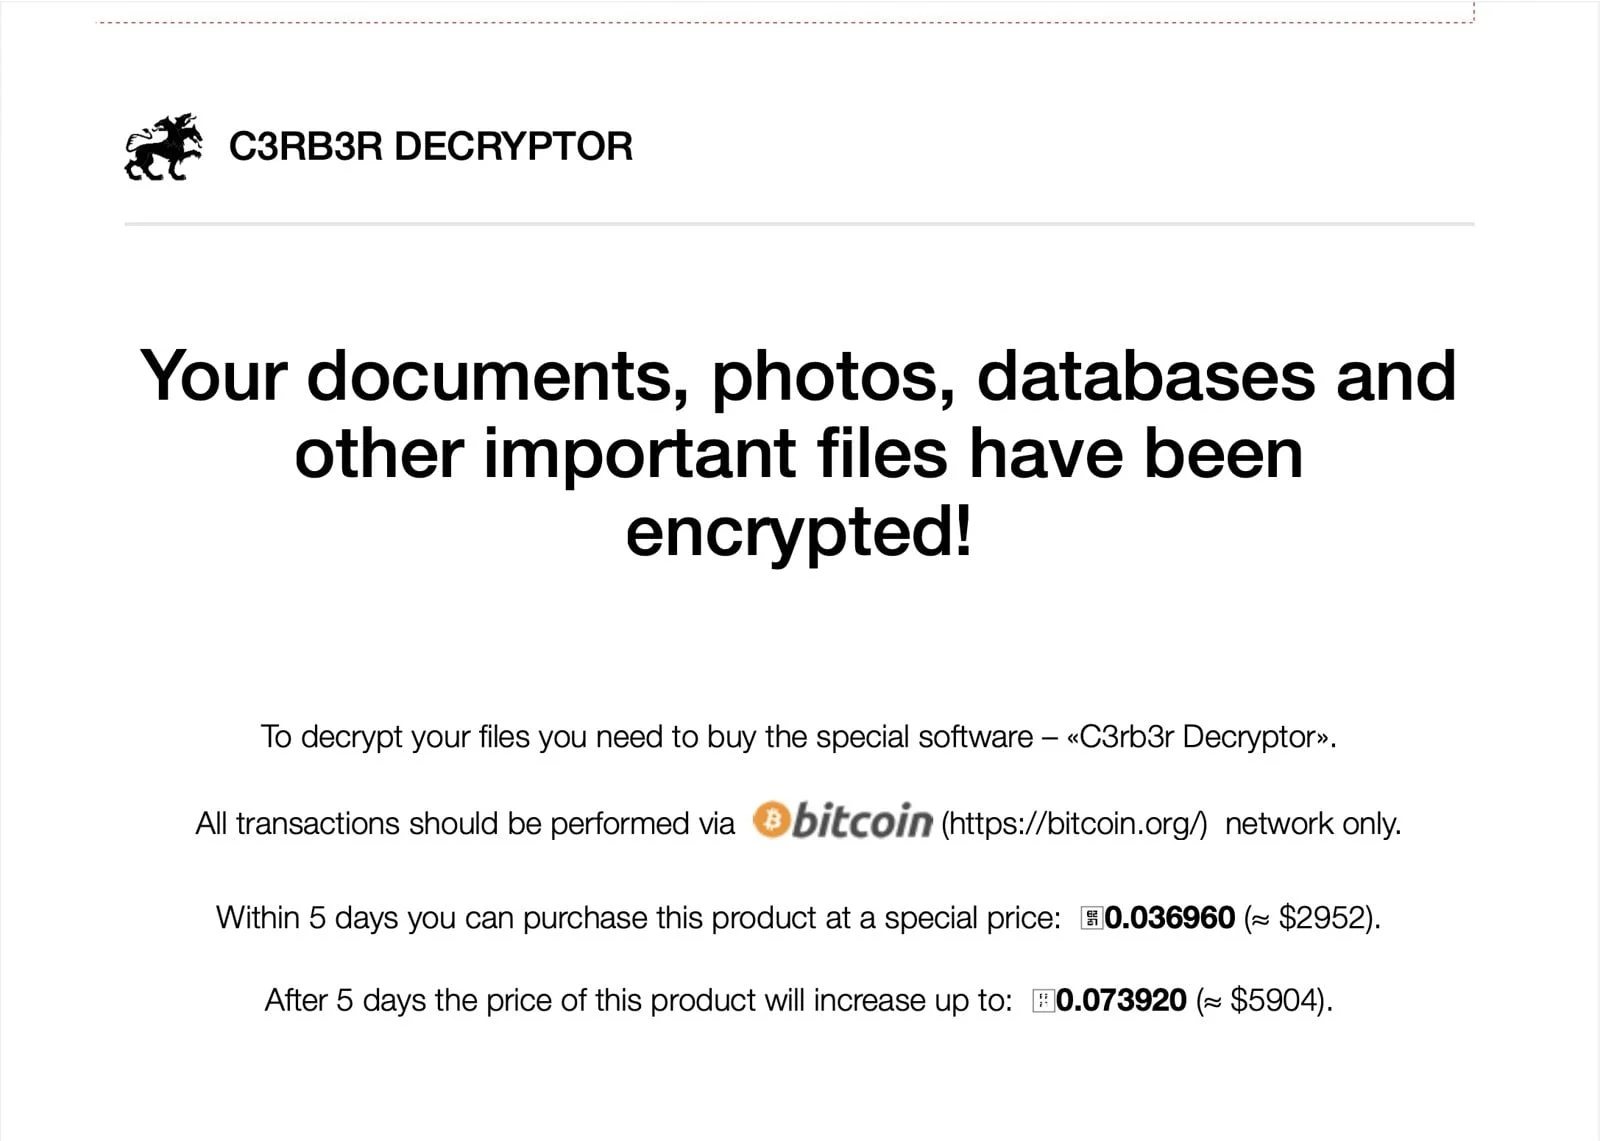
The cover image is a ransom letter demanding bitcoin in the attack on Synology NAS users in Korea using Ransomware, which is currently heating up and has been reported in Vietnam as well. I have an article about this Ransomware on NAS, what to do, where to find the patch, you can read more below. ## Synology warns of ransomware on old DSM NAS: What is ransomware and what do you need to update?

3 min read7,857
Synology warns of ransomware on old DSM NAS: What is ransomware and what do you need to update?

Synology warns of ransomware on old DSM NAS: What is ransomware and what do you need to update?

On Thursday, October 29, 2026, Synology issued a notice advising users to update DSM after a series of ransomware attacks targeting NAS machines still running outdated operating system versions, and the key point is that the attack group is exploiting a vulnerability that the company has patched since December 2024, not a new "super vulnerability" that has not yet been patched. Simply put, this is the type of attacker who takes over, encrypts all of our data, then demands ransom, and must prevent being caught up in wrongful loss of money early. *Yesterday's Synology press release.* ## **What is Ransomware?** Ransomware is a form of ransomware: software that infiltrates a computer or storage device, encrypts the user's files (photos, documents, videos, backups...) so that the person cannot open them again, then displays a notice demanding a ransom if they want the data back.

5 min read4,322
The shadow from the hacker group "The Gentlemen": A red alarm bell for corporate network security

The shadow from the hacker group "The Gentlemen": A red alarm bell for corporate network security

**A cyber security warning has just sent out a worrying signal about the appearance of a hacker group called "The Gentlemen". With double extortion tactics and a countdown timeline, this is a serious threat to the information security infrastructure of businesses.** **The threat called "The Gentlemen" and the double blackmail** According to records from organizations monitoring global cyber security threats, "The Gentlemen" - a hacker group specializing in ransomware attacks - is increasing its activity strongly. This gang's method of operation focuses on the "double extortion" tactic, not only encrypting all internal data to stall operations, but also extracting sensitive information about customer databases, finances and technological secrets.

3 min read4,288