Stolen Fireworks AI Key Triggered Cursor Data Breach and Malicious Extension
Executive Briefing
“The security compromise at coding platform Cursor originated from an access key leaked by...”
Key Takeaways
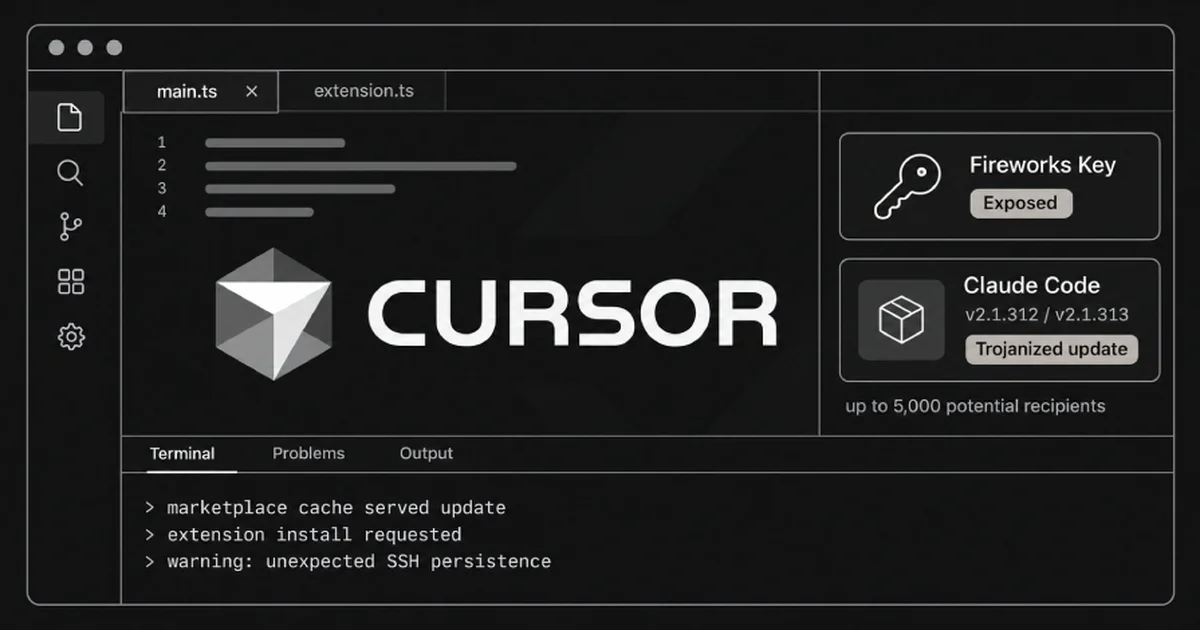
- 1.Cursor confirmed that an access key issued to Fireworks AI was exposed, allowing malicious actors to copy data from a read-only storage bucket.
- 2.The attacker leveraged the acquired sensitive information to breach internal SaaS tools and distribute malicious code into the extension repository on October 29, 2026.
- 3.Approximately 5,000 users potentially received the malicious build aimed at installing an SSH backdoor during an 11-hour window before removal.
The security compromise at coding platform Cursor originated from an access key leaked by third-party vendor Fireworks AI, enabling attackers to distribute a malicious version of the Claude Code extension.
Key Developments and Technical Context
Cursor confirmed that an access key issued to Fireworks AI was exposed, allowing malicious actors to copy data from a read-only storage bucket.
The attacker leveraged the acquired sensitive information to breach internal SaaS tools and distribute malicious code into the extension repository on October 29, 2026.
Approximately 5,000 users potentially received the malicious build aimed at installing an SSH backdoor during an 11-hour window before removal.
Strategic Analysis and Industry Implications
This incident highlights the security risks stemming from third-party supply chains, where a leaked API key at a partner vendor can trigger a chain reaction threatening multiple major infrastructure systems.
Outlook and Key Factors to Watch
The exact scope of damage for all other customers and partners beyond Cursor and Uber utilizing Fireworks AI services remains fully undisclosed.