AWS shares a way to track Amazon Bedrock tokens across accounts
Executive Briefing
“AWS has published a sample design that brings Amazon Bedrock model invocation logs from...”
Key Takeaways
- 1.AWS says it built a centralized lake for Bedrock invocation logs and provides CloudFormation templates, Lambda code and SQL queries in a sample repository.
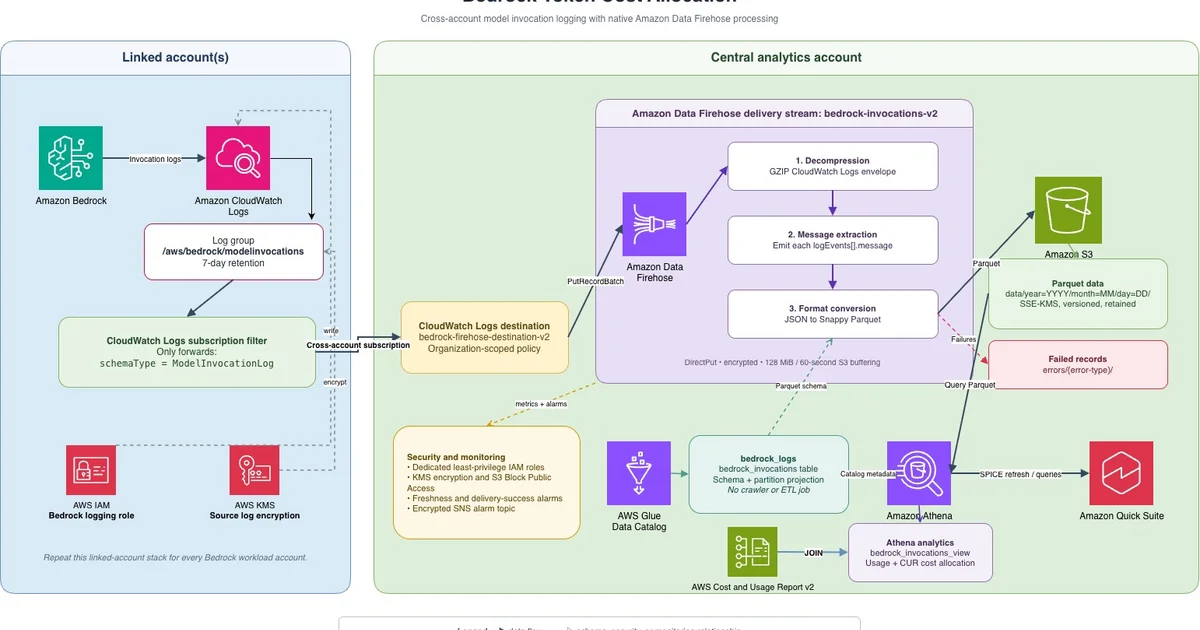
- 2.In AWS’s design, source accounts forward CloudWatch logs to a central account. Amazon Data Firehose processes the data there, and Athena exposes it as a queryable table.
- 3.When invocation logging is enabled, Bedrock can record the model, account, IAM identity, input and output token counts, and request and response text.
- 4.Deploying the infrastructure templates does not itself enable logging. AWS instructs users to activate it separately in each source account.
- 5.AWS describes joining the processed data with its Cost and Usage Report to examine spending by day. Its example queries use an IAM identity ARN as the join key.
AWS has published a sample design that brings Amazon Bedrock model invocation logs from multiple accounts into one place for querying. It can expose token use and the contents of individual calls, but teams must deploy it and enable logging in each source account.
Key Developments and Technical Context
AWS says it built a centralized lake for Bedrock invocation logs and provides CloudFormation templates, Lambda code and SQL queries in a sample repository.
In AWS’s design, source accounts forward CloudWatch logs to a central account. Amazon Data Firehose processes the data there, and Athena exposes it as a queryable table.
When invocation logging is enabled, Bedrock can record the model, account, IAM identity, input and output token counts, and request and response text.
Deploying the infrastructure templates does not itself enable logging. AWS instructs users to activate it separately in each source account.
AWS describes joining the processed data with its Cost and Usage Report to examine spending by day. Its example queries use an IAM identity ARN as the join key.
Strategic Analysis and Industry Implications
Putting token counts alongside models, accounts and request contents could help operations teams identify token-heavy prompts for review. Token counts alone, however, do not show whether a response was useful.
Centralizing prompts and responses also creates a sensitive data store. AWS says the design encrypts stored data and controls access through IAM, while warning that prompts may contain personal information.
Outlook and Key Factors to Watch
The supplied material does not establish the lake’s operating cost or performance at scale.
It also does not establish how precisely the cost-report join attributes spending to individual invocations.