AWS proposes a three-phase roadmap for managing risks in AI agents
Executive Briefing
“AWS has proposed a three-phase roadmap for platform and application teams to manage risks...”
Key Takeaways
- 1.AWS divides the roadmap into three phases and proposes a customizable 12-week implementation timeline. An accompanying scorecard is intended to help platform and application teams reassess their practices as applications mature.
- 2.In the first phase, application teams classify risk for each proposed use case. Platform teams establish monitoring and access controls, while foundational data protections include classification, logging and access monitoring.
- 3.For the pilot, AWS recommends that platform teams establish filters for personally identifiable information in model inputs, outputs and tool calls. Application teams set moderation thresholds for their use cases and arrange human approval for high-risk actions.
- 4.In the final phase, AWS recommends testing whether end-to-end agent workflows treat user groups equitably, evaluating systems before and after deployment, and conducting security tests against agent-specific threats such as prompt injection.
AWS has proposed a three-phase roadmap for platform and application teams to manage risks when deploying AI agents. It moves from governance foundations to a pilot deployment, then evaluation and hardening.
Incident Details & Technical Context
AWS divides the roadmap into three phases and proposes a customizable 12-week implementation timeline. An accompanying scorecard is intended to help platform and application teams reassess their practices as applications mature.
In the first phase, application teams classify risk for each proposed use case. Platform teams establish monitoring and access controls, while foundational data protections include classification, logging and access monitoring.
For the pilot, AWS recommends that platform teams establish filters for personally identifiable information in model inputs, outputs and tool calls. Application teams set moderation thresholds for their use cases and arrange human approval for high-risk actions.
In the final phase, AWS recommends testing whether end-to-end agent workflows treat user groups equitably, evaluating systems before and after deployment, and conducting security tests against agent-specific threats such as prompt injection.
Risk Assessment & Security Implications
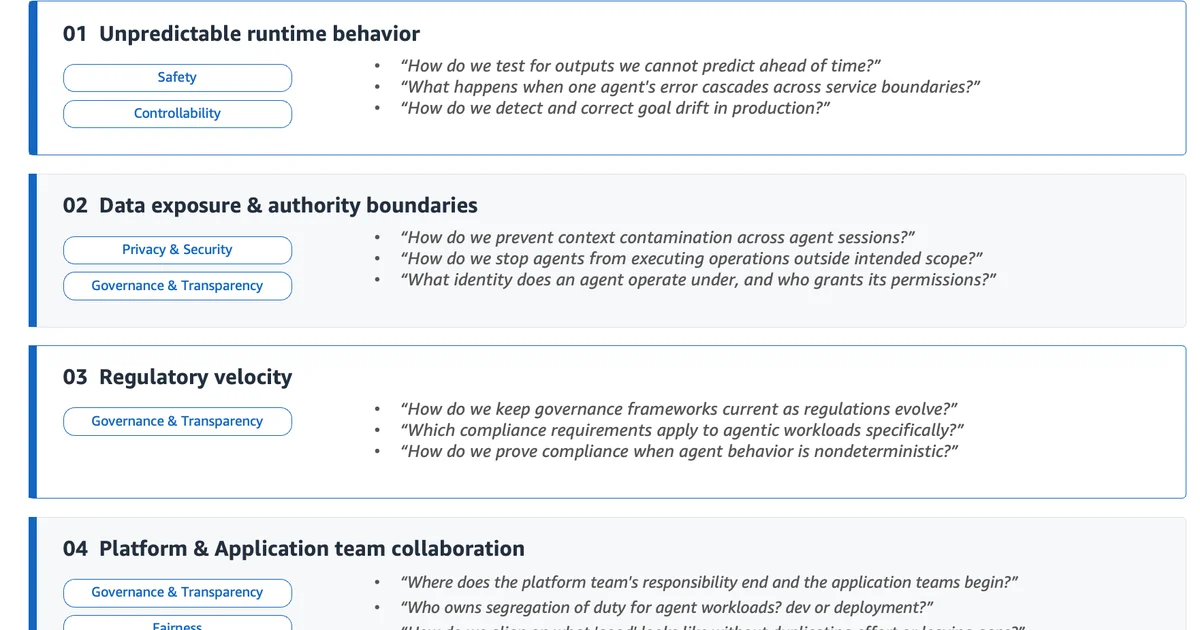
The division of responsibilities could reduce governance gaps. The platform supplies shared access controls and safeguards, but application teams still need to set moderation thresholds and human-review triggers for each agent’s risks.
A pre-launch check alone will not cover later changes to models, tools or data sources. Post-deployment evaluation is useful only if teams use its findings to adjust safeguards and release criteria.
Mitigation & Factors to Watch
The post does not provide step-by-step implementation instructions or legal advice. It therefore does not establish the specific controls or compliance obligations for any particular organization.
The supplied material does not provide measured results showing that adopting the three-phase roadmap reduces incidents in deployed systems.