AIINEWS

AIINEWS

Global intelligence on artificial intelligence and computing

Critical remote code execution flaw in Apache Roller under active exploitation
AIINEWS Editorial Board•security
19 November, 2026•1 min read
Critical remote code execution flaw in Apache Roller under active exploitation

Executive Briefing

“The Java-based blogging platform Apache Roller suffers from a critical security...”

Key Takeaways

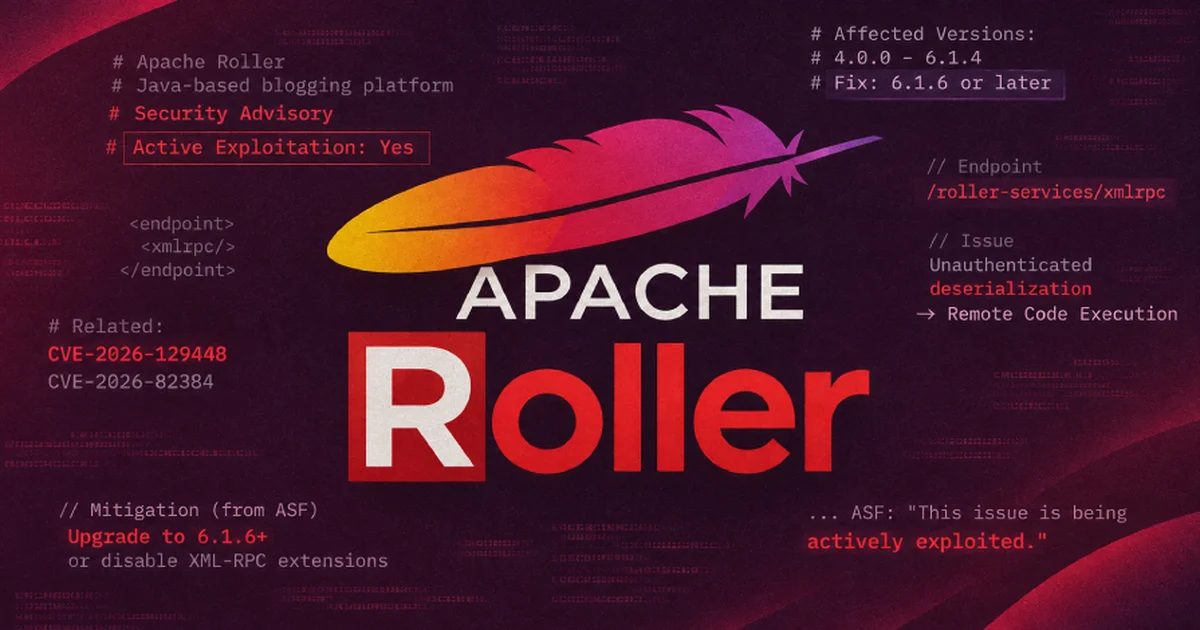
  • 1.Tracked as CVE-2026-129448 with a maximum CVSS score of 9.8, the vulnerability stems from unauthenticated data deserialization at the XML-RPC endpoint.
  • 2.According to the Apache Software Foundation, this weakness is currently being leveraged in active cyberattack campaigns in the wild.
  • 3.Software versions 4.0.0 through 6.1.4 are directly affected because the XML-RPC endpoint accepts vendor extension types before authenticating the requester.
  • 4.System administrators are advised to upgrade to version 6.1.6 or later or adjust configuration files to disable the XML-RPC feature.

The Java-based blogging platform Apache Roller suffers from a critical security vulnerability allowing unauthenticated remote code execution. The Apache Software Foundation urges users to promptly update their software or disable the affected feature.

Incident Details & Technical Context

Tracked as CVE-2026-129448 with a maximum CVSS score of 9.8, the vulnerability stems from unauthenticated data deserialization at the XML-RPC endpoint.

According to the Apache Software Foundation, this weakness is currently being leveraged in active cyberattack campaigns in the wild.

Software versions 4.0.0 through 6.1.4 are directly affected because the XML-RPC endpoint accepts vendor extension types before authenticating the requester.

System administrators are advised to upgrade to version 6.1.6 or later or adjust configuration files to disable the XML-RPC feature.

Risk Assessment & Security Implications

Deserialization flaws in web service endpoints remain a preferred target for attackers because they allow bypassing initial authentication checks to compromise system privileges.

Disabling the feature through the administration interface is insufficient in older versions, requiring administrators to intervene directly in system configuration files.

Mitigation & Factors to Watch

The Apache Software Foundation has not disclosed technical details regarding the exploitation methods used by attackers or the identities of targeted victims.
Independently verified, edited, and published by AIINEWS Editorial Board
3-tier verified
Editorial standards
Share this intelligence report:
Expanded Perspectives & Intelligence

Related Dispatches & Deep Dives

Curated 8 specialized reports
Anti-Oligarchy Activists Plan to Dox Elon Musk and Hundreds of Billionaire-Linked Homes

Anti-Oligarchy Activists Plan to Dox Elon Musk and Hundreds of Billionaire-Linked Homes

An underground activist group says it plans to start openly doxing billionaires as part of a phased campaign against what it calls the American oligarchy—beginning this month with a release that maps the homes of Elon Musk, his brother Kimbal, and Tesla’s board, alongside investors and suppliers that keep the corporation afloat. Two of its members, interviewed by WIRED on the condition of anonymity, say they spent the past year constructing dossiers on billionaires—and one trillionaire—and the people they consider their top lieutenants, using nearly every method available to a private investigator, and some that are not. The pair say the group is international and includes grassroots activists, researchers, journalists, and artists, including some who received top honors in print, television, and digital media in their former careers.

7 min read9,161
The man behind the 'Internet rescue' from the PHP disaster

The man behind the 'Internet rescue' from the PHP disaster

# The man behind the 'Internet rescue' from the PHP disaster Despite being a volunteer, Ondrej Sury played a key role in quickly deploying patches for two PHP2Shell vulnerabilities, which could cause the Internet to crash. "I once told some people, that the world has one expert who alone is responsible for most of the worldwide distribution of PHP. And if anything happens to this person, it's over.

5 min read5,191
Russia recorded an AI self-attack on the network, infiltrating more than 10 servers in 3 hours

Russia recorded an AI self-attack on the network, infiltrating more than 10 servers in 3 hours

According to technology news site *CNews* (Russia) on November 2, cybersecurity experts from the comprehensive cyber threat response department (PT ESC IR) of Positive Technologies Company investigated an attack on a computer system using Linux and Windows of a Russian enterprise. This is the first time PT ESC IR experts have investigated a cyber attack believed to be carried out entirely by artificial intelligence (AI), from intrusion to data theft. According to the company, the attack happened very quickly with many consecutive activities.

3 min read6,234

Explore AIINEWS Intelligence Vault

Over 2,000 in-depth dispatches structured across 18 specialized tech & AI categories.

Browse all 18 categories
Critical remote code execution flaw in Apache Roller under active... | AIINEWS