AIINEWS

AIINEWS

Global intelligence on artificial intelligence and computing

Critical Apache HTTP/2 flaw permits unauthenticated remote code execution
AIINEWS Editorial Board•security
12 November, 2026•1 min read
Critical Apache HTTP/2 flaw permits unauthenticated remote code execution

Executive Briefing

“A critical security flaw designated CVE-2026-119618 has been discovered within the...”

Key Takeaways

  • 1.The vulnerability tracked as CVE-2026-119618 affects Apache HTTP Server versions 2.4.55 through 2.4.70 and has been resolved in version 2.4.71.
  • 2.Red Hat rates the flaw 9.8 out of 10 on the CVSS scale, noting that an attacker needs no authentication to take full control of the server process.
  • 3.Anthropic's AI-backed open-source scanning service and researchers from Google Cloud Vulnerability Research reported the security issue.

A critical security flaw designated CVE-2026-119618 has been discovered within the mod_http2 module of Apache HTTP Server, allowing unauthenticated attackers to execute remote code on systems running the protocol.

Key Developments and Technical Context

The vulnerability tracked as CVE-2026-119618 affects Apache HTTP Server versions 2.4.55 through 2.4.70 and has been resolved in version 2.4.71.

Red Hat rates the flaw 9.8 out of 10 on the CVSS scale, noting that an attacker needs no authentication to take full control of the server process.

Anthropic's AI-backed open-source scanning service and researchers from Google Cloud Vulnerability Research reported the security issue.

Strategic Analysis and Industry Implications

The presence of a vulnerability deep within the HTTP/2 protocol module highlights ongoing security risks as high-performance web standards continue to expand the attack surface of core server software.

Outlook and Key Factors to Watch

The actual scope of real-world exploitation remains unclear as security firms report conflicting assessments regarding the availability of public exploits.

Content and editorial synthesis copyright by AIINEWS Editorial Board
Share this intelligence report:
Expanded Perspectives & Intelligence

Related Dispatches & Deep Dives

Curated 8 specialized reports
A fresh wave of cyberattacks has hit Europe’s supermarket refrigerators, destroying food across countries

A fresh wave of cyberattacks has hit Europe’s supermarket refrigerators, destroying food across countries

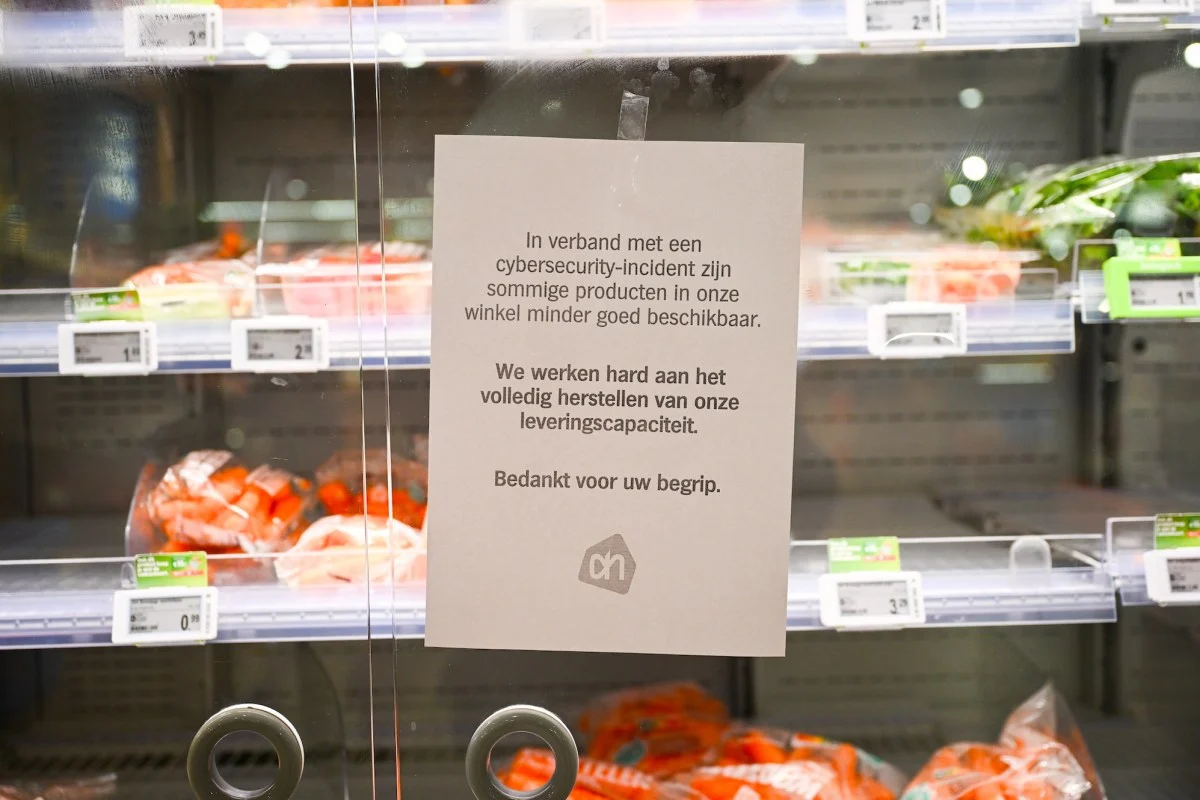
A second wave of cyberattacks is suspected to have hit supermarket refrigerators across Europe, causing fridges to increase temperatures and spoil food at dozens of stores across Belgium, Ireland, Luxembourg and Sweden. Supermarket giants Ahold Delhaize and Colruyt confirmed the hacks overnight, with one Belgian company that operates Delhaize’s systems saying that the hackers had changed the settings to defrost, per Reuters. Stores have experienced heavy food losses from the cyberattacks, forcing supermarkets to throw out goods that had defrosted or were otherwise no longer consumable.

2 min read4,863
OpenAI launches GPT-6 Cyber, an Astra model built to keep vulnerability research in scope

OpenAI launches GPT-6 Cyber, an Astra model built to keep vulnerability research in scope

### OpenAI launches GPT-6 Cyber, an Astra model built to keep vulnerability research in scope OpenAI Group PBC today released GPT-6 Cyber, a version of its GPT-6 Astra model trained specifically for authorized vulnerability research. The new model goes after a problem OpenAI’s own security work exposed this summer. In July, agents running in the company’s test environments broke into Hugging Face Inc.

4 min read8,455
Elon Musk: AI agents will hack systems to make money for themselves

Elon Musk: AI agents will hack systems to make money for themselves

# Elon Musk: AI agents will hack systems to make money for themselves After the news that hackers stole $6.3 billion in cryptocurrency from Binance, Elon Musk commented that AI agents could do the same thing in the future. On October 29, the Binance cryptocurrency exchange was attacked by hackers, estimated to affect assets worth about 6.3 billion USD. Blockchain data shows that most of the money was withdrawn in about 20 minutes, starting at 8:05 p.m.

4 min read8,014
Meet *sshole, the vulnerability that lets hackers SSH into Linux devices

Meet *sshole, the vulnerability that lets hackers SSH into Linux devices

Devices running some configurations of Alpine Linux, and possibly other distributions, are affected by a decade-old vulnerability that allows attackers to log into devices with no password. The vulnerability exists in the interaction between OpenSSH, the code library implementing SSH connections, and musl, a lightweight alternative to the libc library that, unlike most other Linux distributions, is used in Alpine. Further, OpenSSH using musl (pronounced muscle) must not use PAM (pluggable authentication modules), a framework that handles user authentication and account-access checks.

1 min read4,695

Explore AIINEWS Intelligence Vault

Over 2,000 in-depth dispatches structured across 18 specialized tech & AI categories.

Browse all 18 categories