AIINEWS

AIINEWS

Global intelligence on artificial intelligence and computing

Search Intelligence

Query across our knowledge base of synthesized technology dispatches

Results for “vulnerability”23 stories
Meet *sshole, the vulnerability that lets hackers SSH into Linux devices

Meet *sshole, the vulnerability that lets hackers SSH into Linux devices

Devices running some configurations of Alpine Linux, and possibly other distributions, are affected by a decade-old vulnerability that allows attackers to log into devices with no password. The vulnerability exists in the interaction between OpenSSH, the code library implementing SSH connections, and musl, a lightweight alternative to the libc library that, unlike most other Linux distributions, is used in Alpine. Further, OpenSSH using musl (pronounced muscle) must not use PAM (pluggable authentication modules), a framework that handles user authentication and account-access checks.

1 min read5,405
OpenAI launches GPT-6 Cyber, an Astra model built to keep vulnerability research in scope

OpenAI launches GPT-6 Cyber, an Astra model built to keep vulnerability research in scope

### OpenAI launches GPT-6 Cyber, an Astra model built to keep vulnerability research in scope OpenAI Group PBC today released GPT-6 Cyber, a version of its GPT-6 Astra model trained specifically for authorized vulnerability research. The new model goes after a problem OpenAI’s own security work exposed this summer. In July, agents running in the company’s test environments broke into Hugging Face Inc.

4 min read9,715
OpenAI released a new cybersecurity model. Is that enough?

OpenAI released a new cybersecurity model. Is that enough?

Max Justicz, the chief technology officer and cofounder of the startup Charge Robotics, used an OpenAI model to find a severe vulnerability that — if exploited — could allow hackers to take control of servers running Ubuntu, a widely-used open-source Linux based operating system. Justicz, who has a hobbyist’s interest in cybersecurity and previously found a vulnerability in the same codebase, told TechCrunch that he found this issue using GPT 5.6 Sol, released in July, through the AI maker’s Daybreak Blue, a program that gives cybersecurity defenders access to powerful frontier models. “I literally just aimed ChatGPT at the same body of code and said ‘I found this bug previously that was fixed several years ago, please find bugs as bad or worse,’ and it came back in 2 hours with this,” Justicz said.

4 min read9,523
UEFI bootkit infected fully patched Windows machines. Is Microsoft to blame?

UEFI bootkit infected fully patched Windows machines. Is Microsoft to blame?

In 2023, malware tracked as BlackLotus became the first publicly documented in-the-wild UEFI bootkit capable of bypassing Secure Boot on fully updated Windows 11 systems. With the industry-wide chain-of-trust mechanism subverted, the malware was able to run malicious code before Windows was fully loaded and many security defenses were operational. Microsoft had already patched the vulnerability that BlackLotus exploited in 2022.

1 min read4,737
Exclusive: Cogent Security’s VR-1.1 model outscores Claude Code and Codex on vulnerability repair

Exclusive: Cogent Security’s VR-1.1 model outscores Claude Code and Codex on vulnerability repair

### Exclusive: Cogent Security’s VR-1.1 model outscores Claude Code and Codex on vulnerability repair Vulnerability management startup Cogent Security Inc. today released VR-1.1, a new version of its frontier reasoning model that writes fixes for newly disclosed software vulnerabilities. On a public repair benchmark, the model outscored Anthropic PBC’s Claude Code and OpenAI Group PBC’s Codex.

4 min read8,964
Novee’s External Surface Testing checks which exposed assets attackers can actually exploit

Novee’s External Surface Testing checks which exposed assets attackers can actually exploit

### Novee’s External Surface Testing checks which exposed assets attackers can actually exploit Artificial intelligence penetration testing startup Novee Cyber Security Ltd. today added External Surface Testing to its platform so its AI-driven attacks can reach a customer’s entire internet-facing footprint. External Surface Testing is aimed at the scramble after a critical vulnerability is disclosed, when security teams have to work out which exposed assets are affected and whether any can actually be exploited.

3 min read6,303
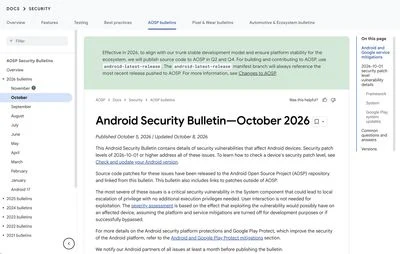
SMS of Death: Android vulnerability allows phone to crash with just one text message

SMS of Death: Android vulnerability allows phone to crash with just one text message

A serious security vulnerability on the Android operating system has just been publicly announced, called "SMS of Death". This vulnerability allows a remote attacker to interrupt mobile connections and interrupt ongoing calls (including emergency calls) simply by sending a special SMS message, without the victim needing to perform any action. The vulnerability is tracked as CVE-2026-58882.

4 min read8,073
The SMS of Death vulnerability causes the signal to crash and hang your Android device just by texting, please update the patch immediately
Gadgets14 days ago

The SMS of Death vulnerability causes the signal to crash and hang your Android device just by texting, please update the patch immediately

The SMS of Death vulnerability causes the signal to crash and hang your Android device just by texting, please update the patch immediately Security researcher Mark Blaszczyk has just announced the vulnerability CVE-2026-58882, named SMS of Death, which allows bad guys to crash Android phones remotely with just a pre-made message, without the recipient needing to click anything. The error lies in the way Android handles WAP Push messages, which run in the background, crashing mobile connections and interrupting calls in progress, including emergency calls. About 20 messages is enough to cause the machine to get stuck in the reboot loop.

3 min read4,271
Synology warns of ransomware on old DSM NAS: What is ransomware and what do you need to update?

Synology warns of ransomware on old DSM NAS: What is ransomware and what do you need to update?

On Thursday, October 29, 2026, Synology issued a notice advising users to update DSM after a series of ransomware attacks targeting NAS machines still running outdated operating system versions, and the key point is that the attack group is exploiting a vulnerability that the company has patched since December 2024, not a new "super vulnerability" that has not yet been patched. Simply put, this is the type of attacker who takes over, encrypts all of our data, then demands ransom, and must prevent being caught up in wrongful loss of money early. *Yesterday's Synology press release.* ## **What is Ransomware?** Ransomware is a form of ransomware: software that infiltrates a computer or storage device, encrypts the user's files (photos, documents, videos, backups...) so that the person cannot open them again, then displays a notice demanding a ransom if they want the data back.

5 min read4,322
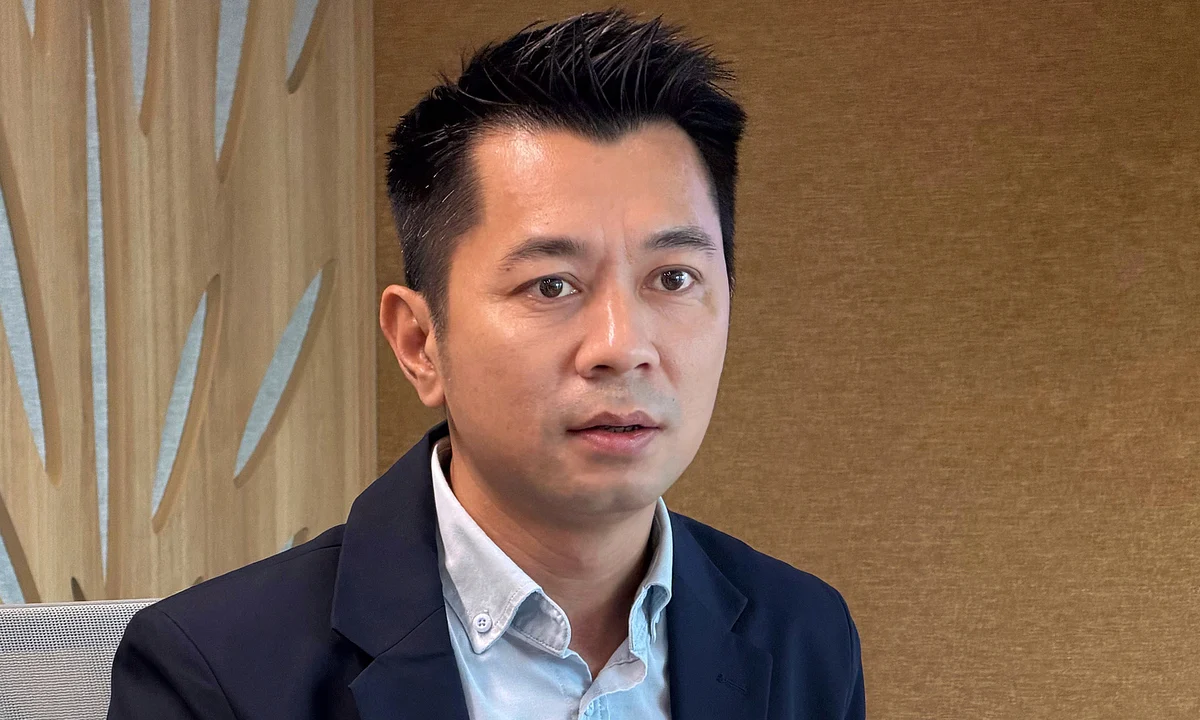
'AI helps hackers exploit vulnerabilities in under a day'

'AI helps hackers exploit vulnerabilities in under a day'

# 'AI helps hackers exploit vulnerabilities in under a day' AI is shortening the time it takes to turn a security vulnerability into an attack tool within 24 hours, while many businesses take 1-2 months to fix, according to a Microsoft representative. According to the Digital Defense Report 2026, published by Microsoft on October 23, Vietnam ranked 7th in the Asia-Pacific region and 20th globally in terms of frequency affected by cyber threat activities in the first half of 2026. The American technology company also assessed that AI is speeding up both offensive and defensive activities in cybersecurity.

5 min read9,692