Hackers exploit N-central flaws to compromise servers running hotfix
Executive Briefing
“N-able implemented additional precautions after security researchers disclosed...”
Key Takeaways
- 1.Independent security researcher Sean Bales disclosed two new vulnerability sets named 4EverAble2Shell and Agent2Shell affecting the latest N-central version.
- 2.The attacks chain a critical Apache Axis vulnerability with a privilege escalation weakness to achieve high-level system access.
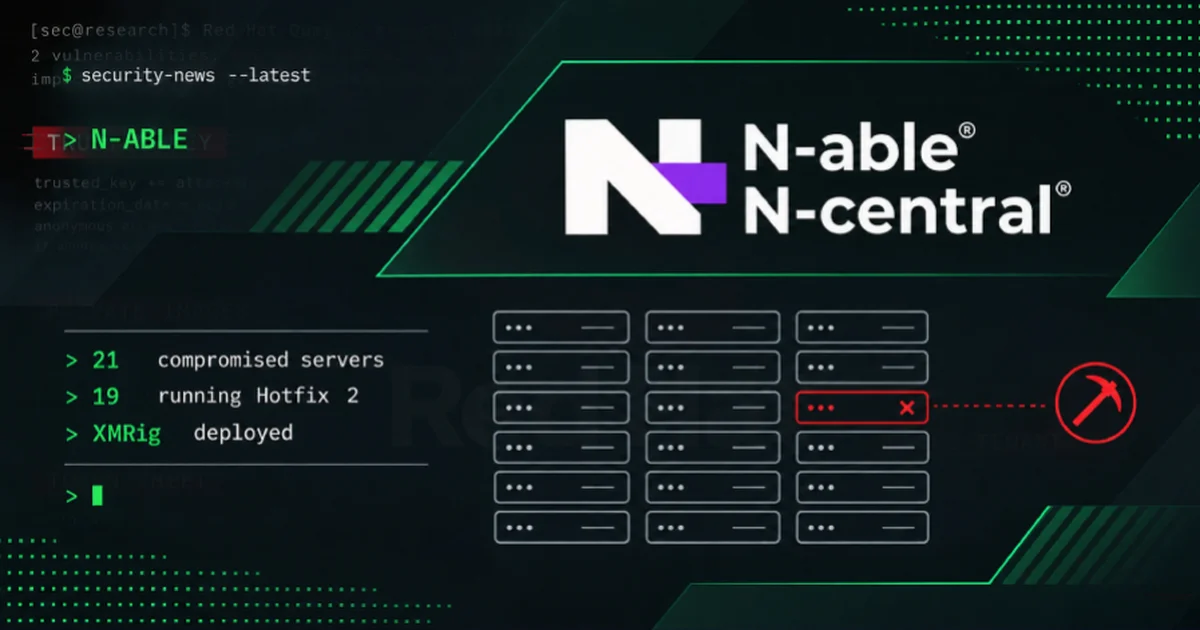
- 3.Cybersecurity firm Huntback discovered that XMRig Monero malware infected 21 N-central servers, including 19 already running Hotfix 2.
N-able implemented additional precautions after security researchers disclosed vulnerabilities allowing attackers to gain system-level access. Cryptocurrency miners successfully infected 21 servers despite most running recent hotfixes.
Key Developments and Technical Context
Independent security researcher Sean Bales disclosed two new vulnerability sets named 4EverAble2Shell and Agent2Shell affecting the latest N-central version.
The attacks chain a critical Apache Axis vulnerability with a privilege escalation weakness to achieve high-level system access.
Cybersecurity firm Huntback discovered that XMRig Monero malware infected 21 N-central servers, including 19 already running Hotfix 2.
Strategic Analysis and Industry Implications
The incident demonstrates that standard software patches alone may be insufficient to stop sophisticated multi-step exploit chains.
Attackers deliberately throttled the CPU usage of the cryptocurrency miner to evade early detection by monitoring tools.
Outlook and Key Factors to Watch
The full scope of actual compromises beyond the 21 servers identified by security firms remains fully unquantified.