Hackers exploit Xen Orchestra auth bypass flaw to gain admin access
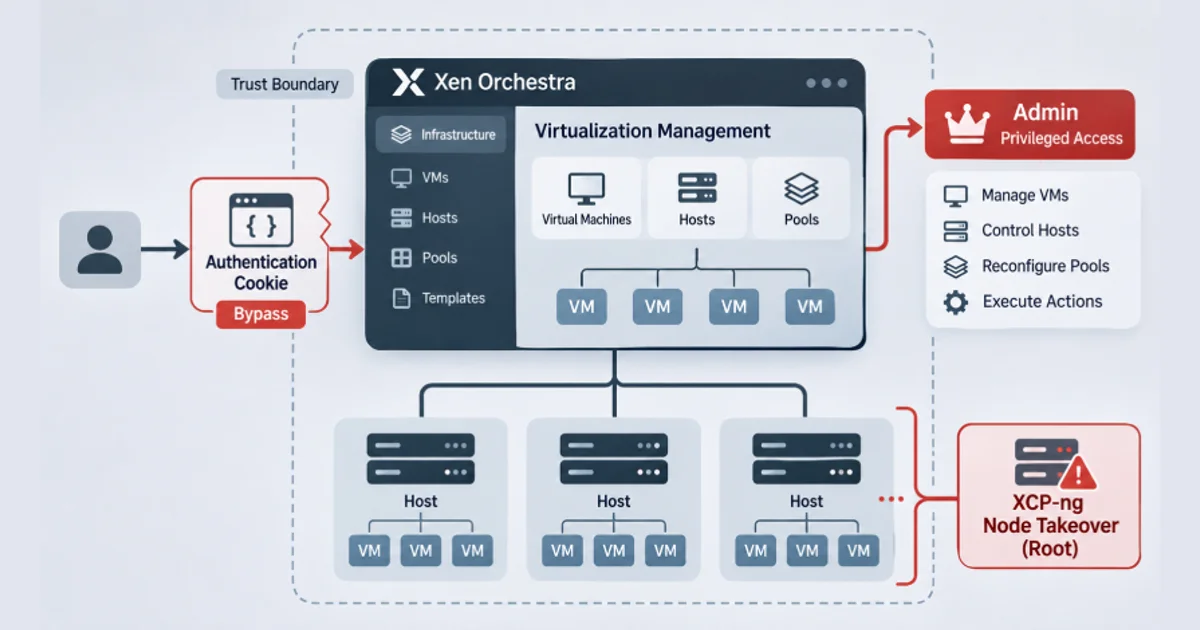
Executive Briefing
“Software firm Vates VMS has warned of a critical security vulnerability in Xen Orchestra...”
Key Takeaways
- 1.Vates VMS reported an authentication bypass vulnerability in Xen Orchestra tracked as VSA-2026-062 without a CVE identifier yet.
- 2.The REST cookie parsing flaw mishandles parameters, causing the token provider to return the first entry in an unfiltered lookup.
- 3.Attackers can leverage this flaw to perform actions with administrator privileges, leading to arbitrary code execution and full node takeover.
- 4.Vates VMS released patched versions including Xen Orchestra 6.9.1 and 6.10.0 alongside xo-server versions 5.211.2 and 5.213.1.
Software firm Vates VMS has warned of a critical security vulnerability in Xen Orchestra that is currently being actively exploited in the wild. The flaw allows attackers to bypass authentication and achieve full administrative control.
Key Developments and Technical Context
Vates VMS reported an authentication bypass vulnerability in Xen Orchestra tracked as VSA-2026-062 without a CVE identifier yet.
The REST cookie parsing flaw mishandles parameters, causing the token provider to return the first entry in an unfiltered lookup.
Attackers can leverage this flaw to perform actions with administrator privileges, leading to arbitrary code execution and full node takeover.
Vates VMS released patched versions including Xen Orchestra 6.9.1 and 6.10.0 alongside xo-server versions 5.211.2 and 5.213.1.
Strategic Analysis and Industry Implications
This vulnerability is exceptionally dangerous as it combines authentication bypass with root-level code execution, enabling threat actors to control managed virtualization infrastructure entirely.
The detailed indicators of compromise provided by Vates VMS help system administrators quickly audit servers and isolate impacted instances.
Outlook and Key Factors to Watch
The exact timeline of when the attack campaign started and whether the vulnerability was exploited as a zero-day remain unclear.