N-able Patches 17 N-central Flaws While Attackers Exploit Earlier Bugs
N-able released a critical security update addressing 17 flaws in N-central as malicious actors actively exploit earlier vulnerabilities to deploy cryptocurrency miners.
Global intelligence on artificial intelligence and computing
Query across our knowledge base of synthesized technology dispatches

N-able released a critical security update addressing 17 flaws in N-central as malicious actors actively exploit earlier vulnerabilities to deploy cryptocurrency miners.

Amazon reported that automated AI agents have been hunting for vulnerabilities in internet-exposed AI applications such as LiteLLM and Dify to harvest provider keys. The campaign leverages an open-source penetration testing tool named ARTEX to exploit default configurations and unpatched flaws.

Google Threat Intelligence Group reported that attackers deployed a fully autonomous artificial intelligence framework to turn security patches into working exploits without human intervention. The system continuously compares application code before and after patch disclosures to draft and execute attacks.

Google says attackers are using large language models and AI agents to analyze patches and develop exploits faster. It has also observed groups experimenting with multi-agent tools that automate parts of an intrusion.

A critical security vulnerability in MongoDB servers can be exploited to crash database instances during failover events. The vendor has released emergency patches to address the issue.

Google Cloud announced that virtual machines running on AMD Turin chips require a guest OS patch and a full stop-and-start cycle to block three transient scheduler side-channel flaws.

Blackpoint Cyber found that the SCKit toolkit tries to turn a ScreenConnect-managed endpoint into a route to a technician’s workstation. The researchers say the existing patch blocks its vulnerability exploit, but a compromised operator session could still be abused.

Threat actors are exploiting unpatched vulnerabilities in Check Point security gateways to gain initial access, escalate privileges, and execute destructive data wiper campaigns targeting organizations globally.

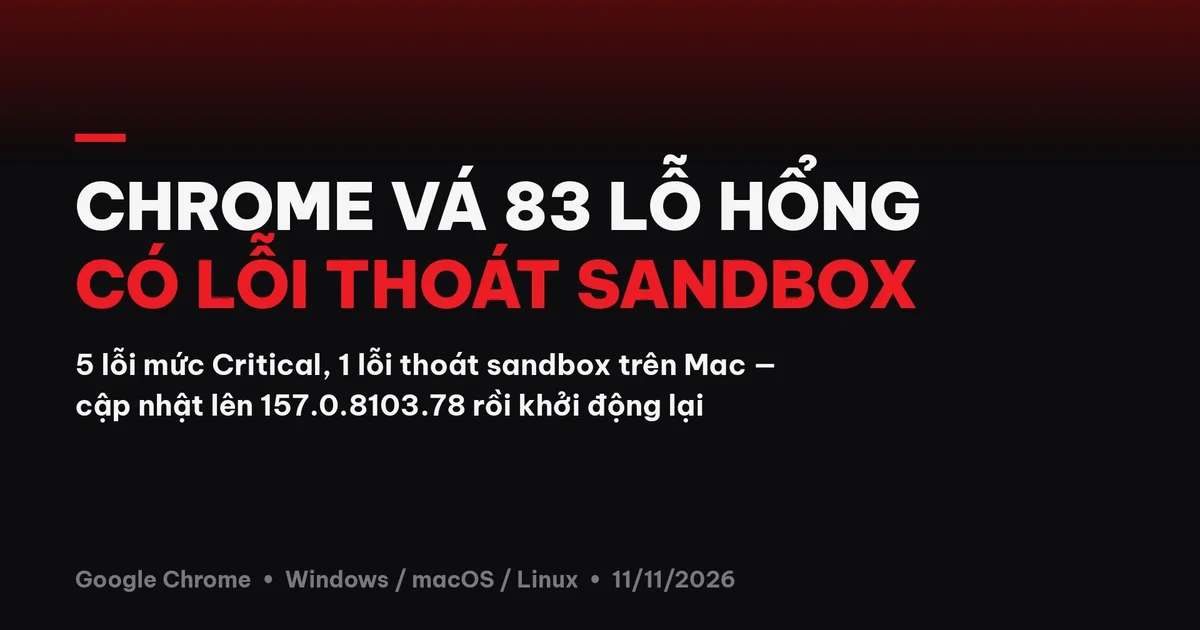
Google has released Chrome version 157.0.8103.78 to address 83 security vulnerabilities across multiple operating systems. This update includes five critical flaws and a notable sandbox escape vulnerability on Mac computers.

Microsoft has released patches for 1,259 security vulnerabilities across its software portfolio, marking the second consecutive month patch volumes exceeded one thousand. The update addresses a moderate-severity Outlook flaw that is actively being exploited and threatens to expose authentication credentials.

The U.S. Cybersecurity and Infrastructure Security Agency added two security vulnerabilities affecting Cisco BroadWorks and Openwave systems to its catalog of known exploited flaws. Officials instructed government agencies to apply patches before late November 2026.

Google has rolled out an emergency security update addressing nine vulnerabilities in Chrome, including a dangerous memory flaw currently under active exploitation in the wild. This marks the eighth actively exploited zero-day vulnerability patched in the browser since the beginning of 2026.

### ZDNET’s key takeaways - An ancient bug is affecting Alpine Linux and a few other Linux distros. - It’s about as bad as it can get. - You must patch ASAP, and then restart the patched software.

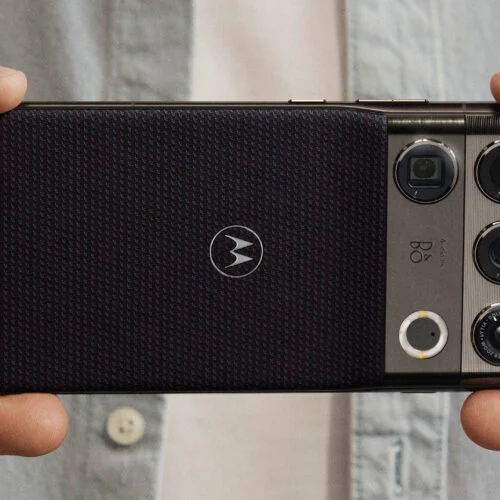
Motorola is patching a hole in its US lineup with a non-folding flagship phone, but the pricing puts this device dangerously close to the company's expensive tablet-style foldable. The long-rumored Motorola Signature 27 is real, featuring top-of-the-line specs, a super-bright OLED screen, and a ton of cameras. But all this high-end hardware won't come cheap in the age of AI.

Hackers possibly linked to the Kremlin exploited previously patched iOS and Android flaws in an attempt to hack visitors of multiple websites, including one celebrating the 250th anniversary of the signing of the US Constitution, researchers said Wednesday. The attackers, which the researchers assessed with “moderate to high confidence” were part of Russia’s Foreign Intelligence Service, targeted other sites, many with links to that country’s ongoing war against Ukraine. The attacks began when iPhone or Android users visited one of potentially hundreds of different sites.

Frontier AI models that uncover software flaws by the hundreds are forcing database providers into larger, faster patch cycles, and real application testing is becoming the safeguard that keeps those fixes from breaking production systems. The same AI wave is also undermining security rules written into applications. Oracle Corp. has responded on two fronts, hardening […] The post Oracle connects AI-driven testing with a new approach to database security appeared first on SiliconANGLE.

**This Vietnamese scientist was elected to the senior member class of the American Academy of Inventors (NAI) in 2024.** From the microneedle patch that can deliver vaccines into the body without needing multiple injections to the biodegradable ultrasound device that helps deliver drugs to the brain, Associate Professor Dr. Nguyen Duc Thanh's research contributes to the process of opening up new approaches in medicine. The Vietnamese scientist has attracted tens of millions of dollars in funding and is named in the Academy of American Inventors.

In 2023, malware tracked as BlackLotus became the first publicly documented in-the-wild UEFI bootkit capable of bypassing Secure Boot on fully updated Windows 11 systems. With the industry-wide chain-of-trust mechanism subverted, the malware was able to run malicious code before Windows was fully loaded and many security defenses were operational. Microsoft had already patched the vulnerability that BlackLotus exploited in 2022.

The SMS of Death vulnerability causes the signal to crash and hang your Android device just by texting, please update the patch immediately Security researcher Mark Blaszczyk has just announced the vulnerability CVE-2026-58882, named SMS of Death, which allows bad guys to crash Android phones remotely with just a pre-made message, without the recipient needing to click anything. The error lies in the way Android handles WAP Push messages, which run in the background, crashing mobile connections and interrupting calls in progress, including emergency calls. About 20 messages is enough to cause the machine to get stuck in the reboot loop.

Meta is planning to release the last OS update for its Quest 2 and Quest Pro VR headsets by March 2027, the company announced today. The last OS update for those devices is planned to be v213, and after that, Meta will continue to ship security patches and critical bug fixes through the end of 2027. Apps that support the Quest 2 or Quest Pro can also be submitted through December 2027, Meta says.

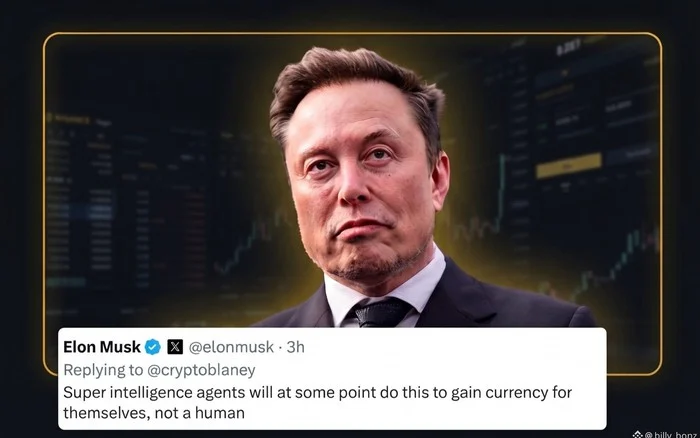
**Elon Musk predicts that super-intelligent AI agents could exploit financial system vulnerabilities to make money for themselves, instead of serving humans.** In a new comment on his X page, the American technology billionaire wrote: *“At some point, superintelligent agents will do the same thing to make money for themselves, not for humans.”* The statement came after hackers used crypto assets stolen from Binance as collateral on decentralized finance platform Aave to borrow Ether. According to LlamaRisk analysis, one wallet involved in the attack deposited 60 million USDT into Aave V3 and borrowed 19,762 WETH, worth approximately $44.6 million at the time of the transaction. According to Bernardo Brites, CEO of Trace Finance, AI tools are now capable of finding security vulnerabilities faster than engineering teams can patch them.

**MSI MPG 341CQR QD-OLED **Design and stand worth the price** If you have ever used MPG 341CQPX or MAG 341CQP, you will find the X36 familiar at first sight. It's still rough black plastic interspersed with glossy patches, the back has a scratched metal finish with a glossy logo in the middle, the screen border is thin and the body is surprisingly thin for a curved panel, only about 7 mm on both edges. Under the chin of the screen is a small strip containing the AI Care logo and sensor.

Anthropic, OpenAI, Cloudflare and Google now each ship an AI agent that hunts security bugs in source code. We checked the repos, docs and technical details behind each one. The key finding: all 4 tools converge on one design.

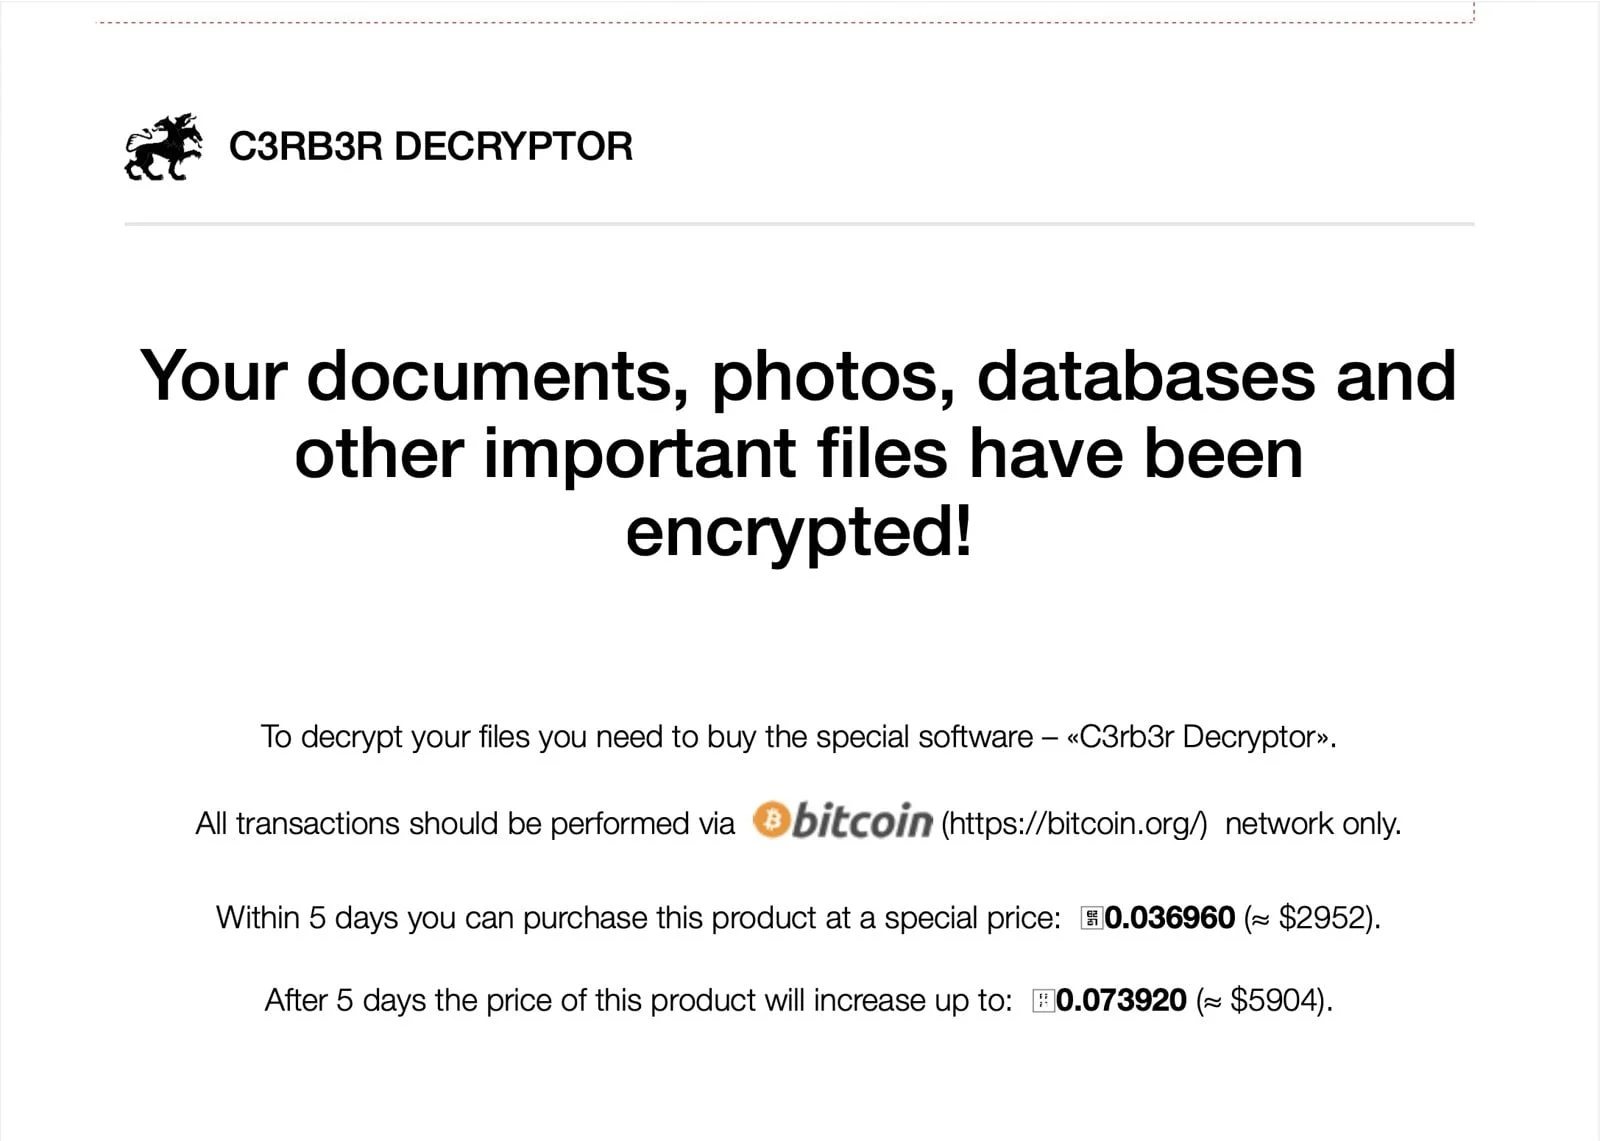
The cover image is a ransom letter demanding bitcoin in the attack on Synology NAS users in Korea using Ransomware, which is currently heating up and has been reported in Vietnam as well. I have an article about this Ransomware on NAS, what to do, where to find the patch, you can read more below. ## Synology warns of ransomware on old DSM NAS: What is ransomware and what do you need to update?