Over 35000 Grok built applications exposed online with sensitive data
Executive Briefing
“Security firm Claroc discovered over 35000 applications generated by the Grok AI tool...”
Key Takeaways
- 1.Security firm Claroc found 37571 Grok-built applications online, with 35578 open to anyone without requiring a sign-in.
- 2.The exposed apps included 24 items built by staff at social network X and Grok creator SpaceXSI, holding internal documents such as onboarding plans and advertising proposals.
- 3.Roughly 2% of the open apps contained material serious enough to rate as high or critical, including a fire department shift board, hospital employee lists, and source code holding plain-text passwords.
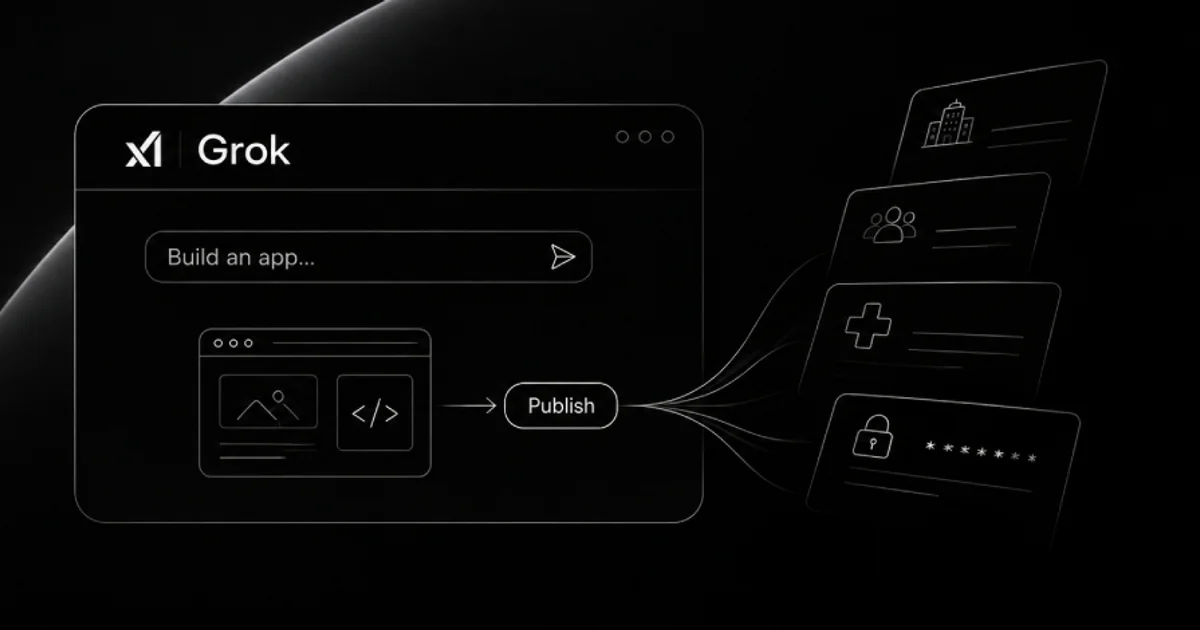
- 4.The Grok app builder's default setting preselected sharing with anyone holding the link, combined with subdomains being recorded via passive DNS lookup services.
Security firm Claroc discovered over 35000 applications generated by the Grok AI tool exposed online without requiring authentication, leaving numerous instances leaking sensitive internal data and personal credentials.
Key Developments and Technical Context
Security firm Claroc found 37571 Grok-built applications online, with 35578 open to anyone without requiring a sign-in.
The exposed apps included 24 items built by staff at social network X and Grok creator SpaceXSI, holding internal documents such as onboarding plans and advertising proposals.
Roughly 2% of the open apps contained material serious enough to rate as high or critical, including a fire department shift board, hospital employee lists, and source code holding plain-text passwords.
The Grok app builder's default setting preselected sharing with anyone holding the link, combined with subdomains being recorded via passive DNS lookup services.
Strategic Analysis and Industry Implications
This incident illustrates a severe security risk when artificial intelligence software creation tools default to permissive access rather than strict privacy. Allowing non-technical users to deploy applications without access control knowledge creates large-scale corporate vulnerabilities.
Outlook and Key Factors to Watch
Whether SpaceXSI will notify external organizations whose apps were exposed remains unclear from the company's initial response.
The full extent of actual data compromise resulting from unauthorized access to the exposed code repositories and databases outside the research team has not been fully quantified.